Your Next Cyberattack Could Sound Like Your CEO
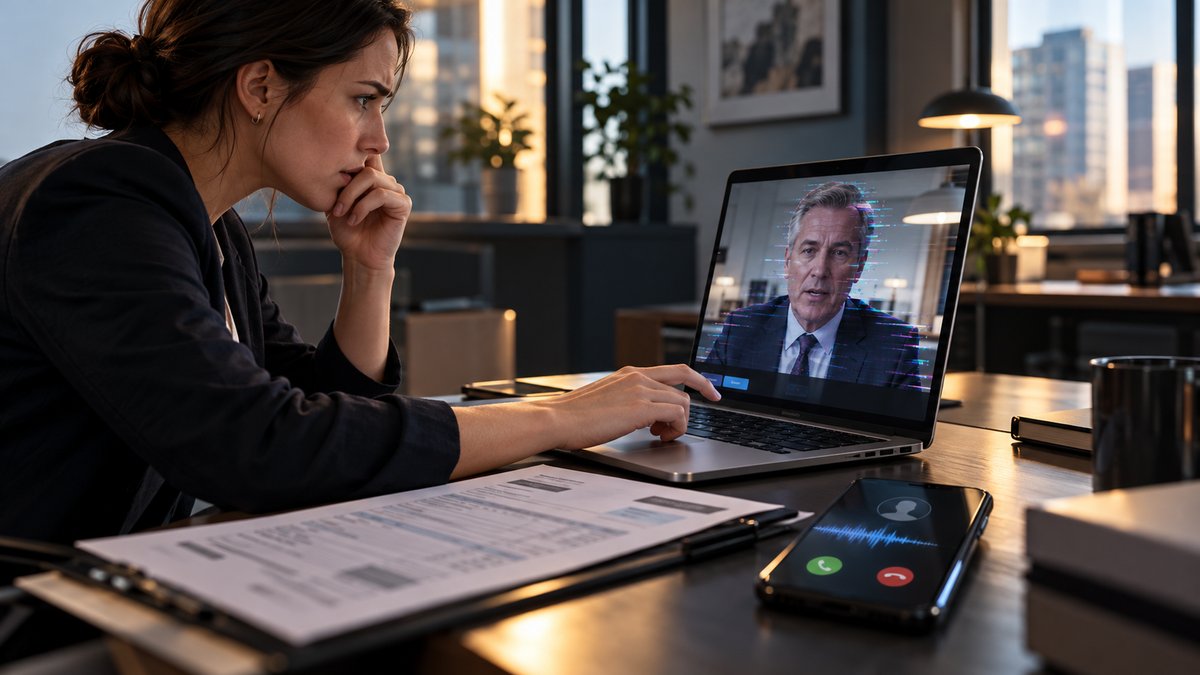
The call comes during a busy afternoon. The voice sounds familiar: your CEO is in a meeting, needs a supplier paid today, and asks you to keep the request confidential. The caller knows the project name and the finance manager’s first name. The urgency feels real.
But the voice may be generated by AI. And the request may be a scam.
Voice cloning tools can imitate a person from audio that is already available online or shared in meetings. Criminals can use a cloned voice to pressure an employee into sending money, changing payment details, or revealing sensitive information. A convincing voice is no longer proof of identity.
The same tactic can appear in a familiar-looking invoice. A fraudster may pose as a regular vendor and send a message claiming the company’s bank details have changed. The invoice may use the right logo, project description, and payment amount. If an employee acts quickly without checking the change, the money can go to an account controlled by the criminal.
Deepfake video calls add another layer. A familiar face on screen may appear to confirm an urgent payment or authorize access. Yet video can be manipulated, and a caller’s appearance should not replace established approval procedures.
Companies without dedicated security teams can still make these attacks harder to pull off. The most useful safeguards are simple, consistent steps that employees follow every time.
Verify requests through a second channel. If a call or email asks for a payment, password, gift card, or change to vendor banking details, pause and contact the person using a phone number or contact record already on file. Don’t use the number or link in the new message. For a high-value payment, require confirmation from a second authorized person.
Set a clear rule for payment changes. Treat every request to update bank details as high risk. Verify it with the vendor using a known phone number, and document who confirmed the change. Keep vendor setup and payment approval with different people when possible.
Use a private verification phrase for urgent requests. Leadership can agree on a phrase or a simple callback procedure for unusual financial or sensitive requests. Keep the phrase out of public posts and routine email. The goal is a reliable check, not a secret that employees share widely.
Slow down pressure. “Act now,” “don’t tell anyone,” and “I can’t talk” are reasons to pause, not reasons to skip review. Make it clear that staff will not be punished for delaying an unusual request while they verify it.
Protect accounts with multifactor authentication. Require it for email, banking, payroll, and other important systems. Use unique passwords stored in a password manager, and remove access promptly when employees or contractors leave.
Practice what to do. A short staff meeting can walk through a fake invoice-change request or a supposed executive call. Give employees a simple way to report suspicious messages, such as forwarding them to a designated manager. Make sure everyone knows that reporting a near miss is helpful, not embarrassing.
Small businesses often rely on trust and quick decisions to get work done. Criminals try to exploit both. A familiar voice, an executive’s face, or a polished invoice can all be copied. A pause, a callback to a verified number, and a second approval can interrupt the scam before money or access is lost.
The best first response to an urgent request may be a simple question: “Can I call you back on the number we already have?”